 Human-centered IT
Cybersecurity, physical security, and proactive alerting, treated as one connected discipline.
We try to break into your systems on purpose, then tell you exactly how, and how to fix it.
Ongoing, senior-level security leadership and strategy, without the cost of a full-time executive hire.
We train your team to spot the tricks attackers actually use, then test them with realistic simulated attempts.
Cameras, alarms, and the physical safeguards that protect your people and property, not just your network.
Badge systems, locks, and visitor policies that control exactly who can get into your building and where.
We watch your systems around the clock and flag suspicious activity before it turns into an incident.
We start with a security assessment and, where useful, a penetration test to see your environment the way an attacker would.
Findings become a prioritized plan covering technical controls, physical security, and leadership gaps.
We implement the fixes, or step in directly as your vCISO if you need ongoing security leadership.
Proactive SOC/SIEM monitoring and alerting keep watch after the engagement ends, not just during it.
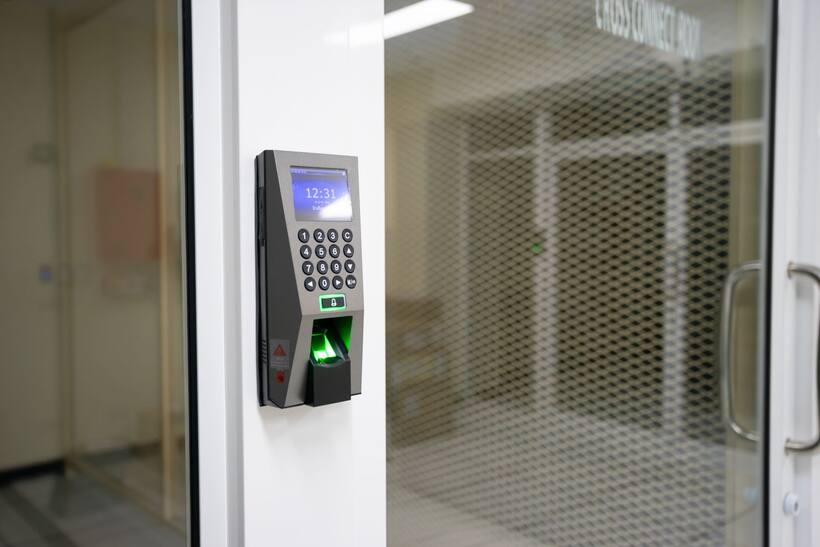
A locked-down network doesn't mean much if the server room door doesn't lock too. We treat physical access control, monitoring, and cybersecurity as one perimeter, not three separate vendors to reconcile.
No formal security leadership and limited visibility into active threats.
Prodigy stood up a vCISO retainer alongside proactive SOC/SIEM monitoring and a baseline penetration test.
Established ongoing security leadership, and caught and contained an intrusion attempt within its first year of coverage.
Yes, alongside broader security assessments that look at your environment the way an attacker would, not just against a checklist.
A Virtual CISO retainer gives you ongoing, senior-level security leadership, without the cost of a full-time executive hire.
Both. We treat physical security and facility access control as part of the same risk picture as your network and data.
We provide proactive SOC/SIEM monitoring, so threats get flagged and acted on before they become incidents, not after.
Tell us what you're working on, and we'll point you to the right discipline.